Using external Secrets for application deployment
Overview
If you want deploy Adeptia Automate using external secrets instead of the plaintext ones stored in the values.yaml file, you can leverage HashiCorp Vault to achieve the purpose. This approach enhances security by avoiding the risk of exposing secrets or credentials in a file.
This document outlines the processes occurring in the background when you configure values.yaml to retrieve imagePullSecrets and database credentials from HashiCorp Vault.
Prerequisites
Before you begin to deploy Adeptia Automate using the secrets from HashiCorp vault, ensure that you have the required administrative privileges to deploy additional Custom Resource Definitions (CRDs).
Components
- HashiCorp Vault: A tool for securely managing secrets.
- Kubernetes Cluster: The environment where Adeptia Automate is deployed.
- External Secrets Pod: A pod responsible for requesting and receiving secrets from HashiCorp Vault.
- External Secrets Resource: A custom resource in Kubernetes that stores the secrets received from the External Secrets pod.
- Secrets Resource: Kubernetes resource used to reference and manage secrets within the cluster.
- Adeptia Automate Microservices Pods: Application pods that require secrets to function.
How it works
The following diagram depicts how the external secrets are fetched and used for the deployment of Adeptia Automate.
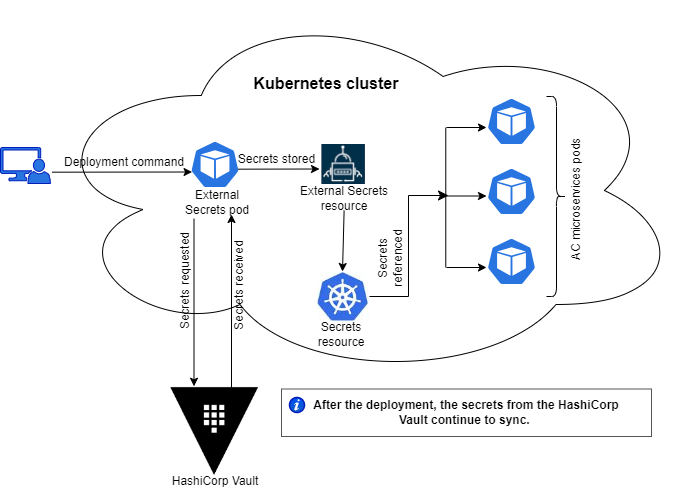
- Deployment Command Initiated:
- The user runs the command to deploy the application.
- External Secret pod spins up:
- An External Secrets pod spins up in the Kubernetes cluster.
- Secrets Requested:
- The External Secrets pod sends a request to HashiCorp Vault to retrieve the imagePullSecrets and database credentials.
- Secrets Received:
- HashiCorp Vault responds to the request by sending the requested secrets to the External Secrets pod.
- Secrets Stored:
- The External Secrets pod stores the received secrets in the External Secrets resource within the Kubernetes cluster.
- Secrets Referenced:
- The stored secrets go to the Kubernetes Secrets resource and the Adeptia Automate microservices pods reference this resource to access the necessary secrets for their operations.
Continuous Sync
-
After the initial deployment, the secrets from HashiCorp Vault continue to sync with the Kubernetes cluster. Any changes made to the secrets in HashiCorp Vault are automatically updated in the External Secrets resource and consequently in the Secrets resource.

In case, there are any changes in the imagePullSecrets or database credentials, you need to restart the pods to bring the changes into effect.